Repository navigation
fix(mcp): Let browsers send Origin on the consent POST - #2638
Merged
Merged
Conversation


The consent page set Referrer-Policy: no-referrer. Under that policy,
browsers send Origin: null on a form POST, so the same-origin check
rejected every Allow click with "Request blocked". Use same-origin
instead: the consent POST keeps its Origin, and the cross-origin
redirect to the client still gets no referrer.

The test fixture now derives Origin from the page's referrer policy the
way a browser does, so the integration test catches this.

Co-Authored-By: David Cramer <23610+dcramer@users.noreply.github.com>

|
The latest updates on your projects. Learn more about Vercel for GitHub.
|


Contributor
|
2 screenshot changes — 2 changed · 0 added · 0 removed Review screenshots in Frameshift
|

dcramer
approved these changes
Nov 4, 2026

dcramer
added a commit
that referenced
this pull request
Nov 4, 2026
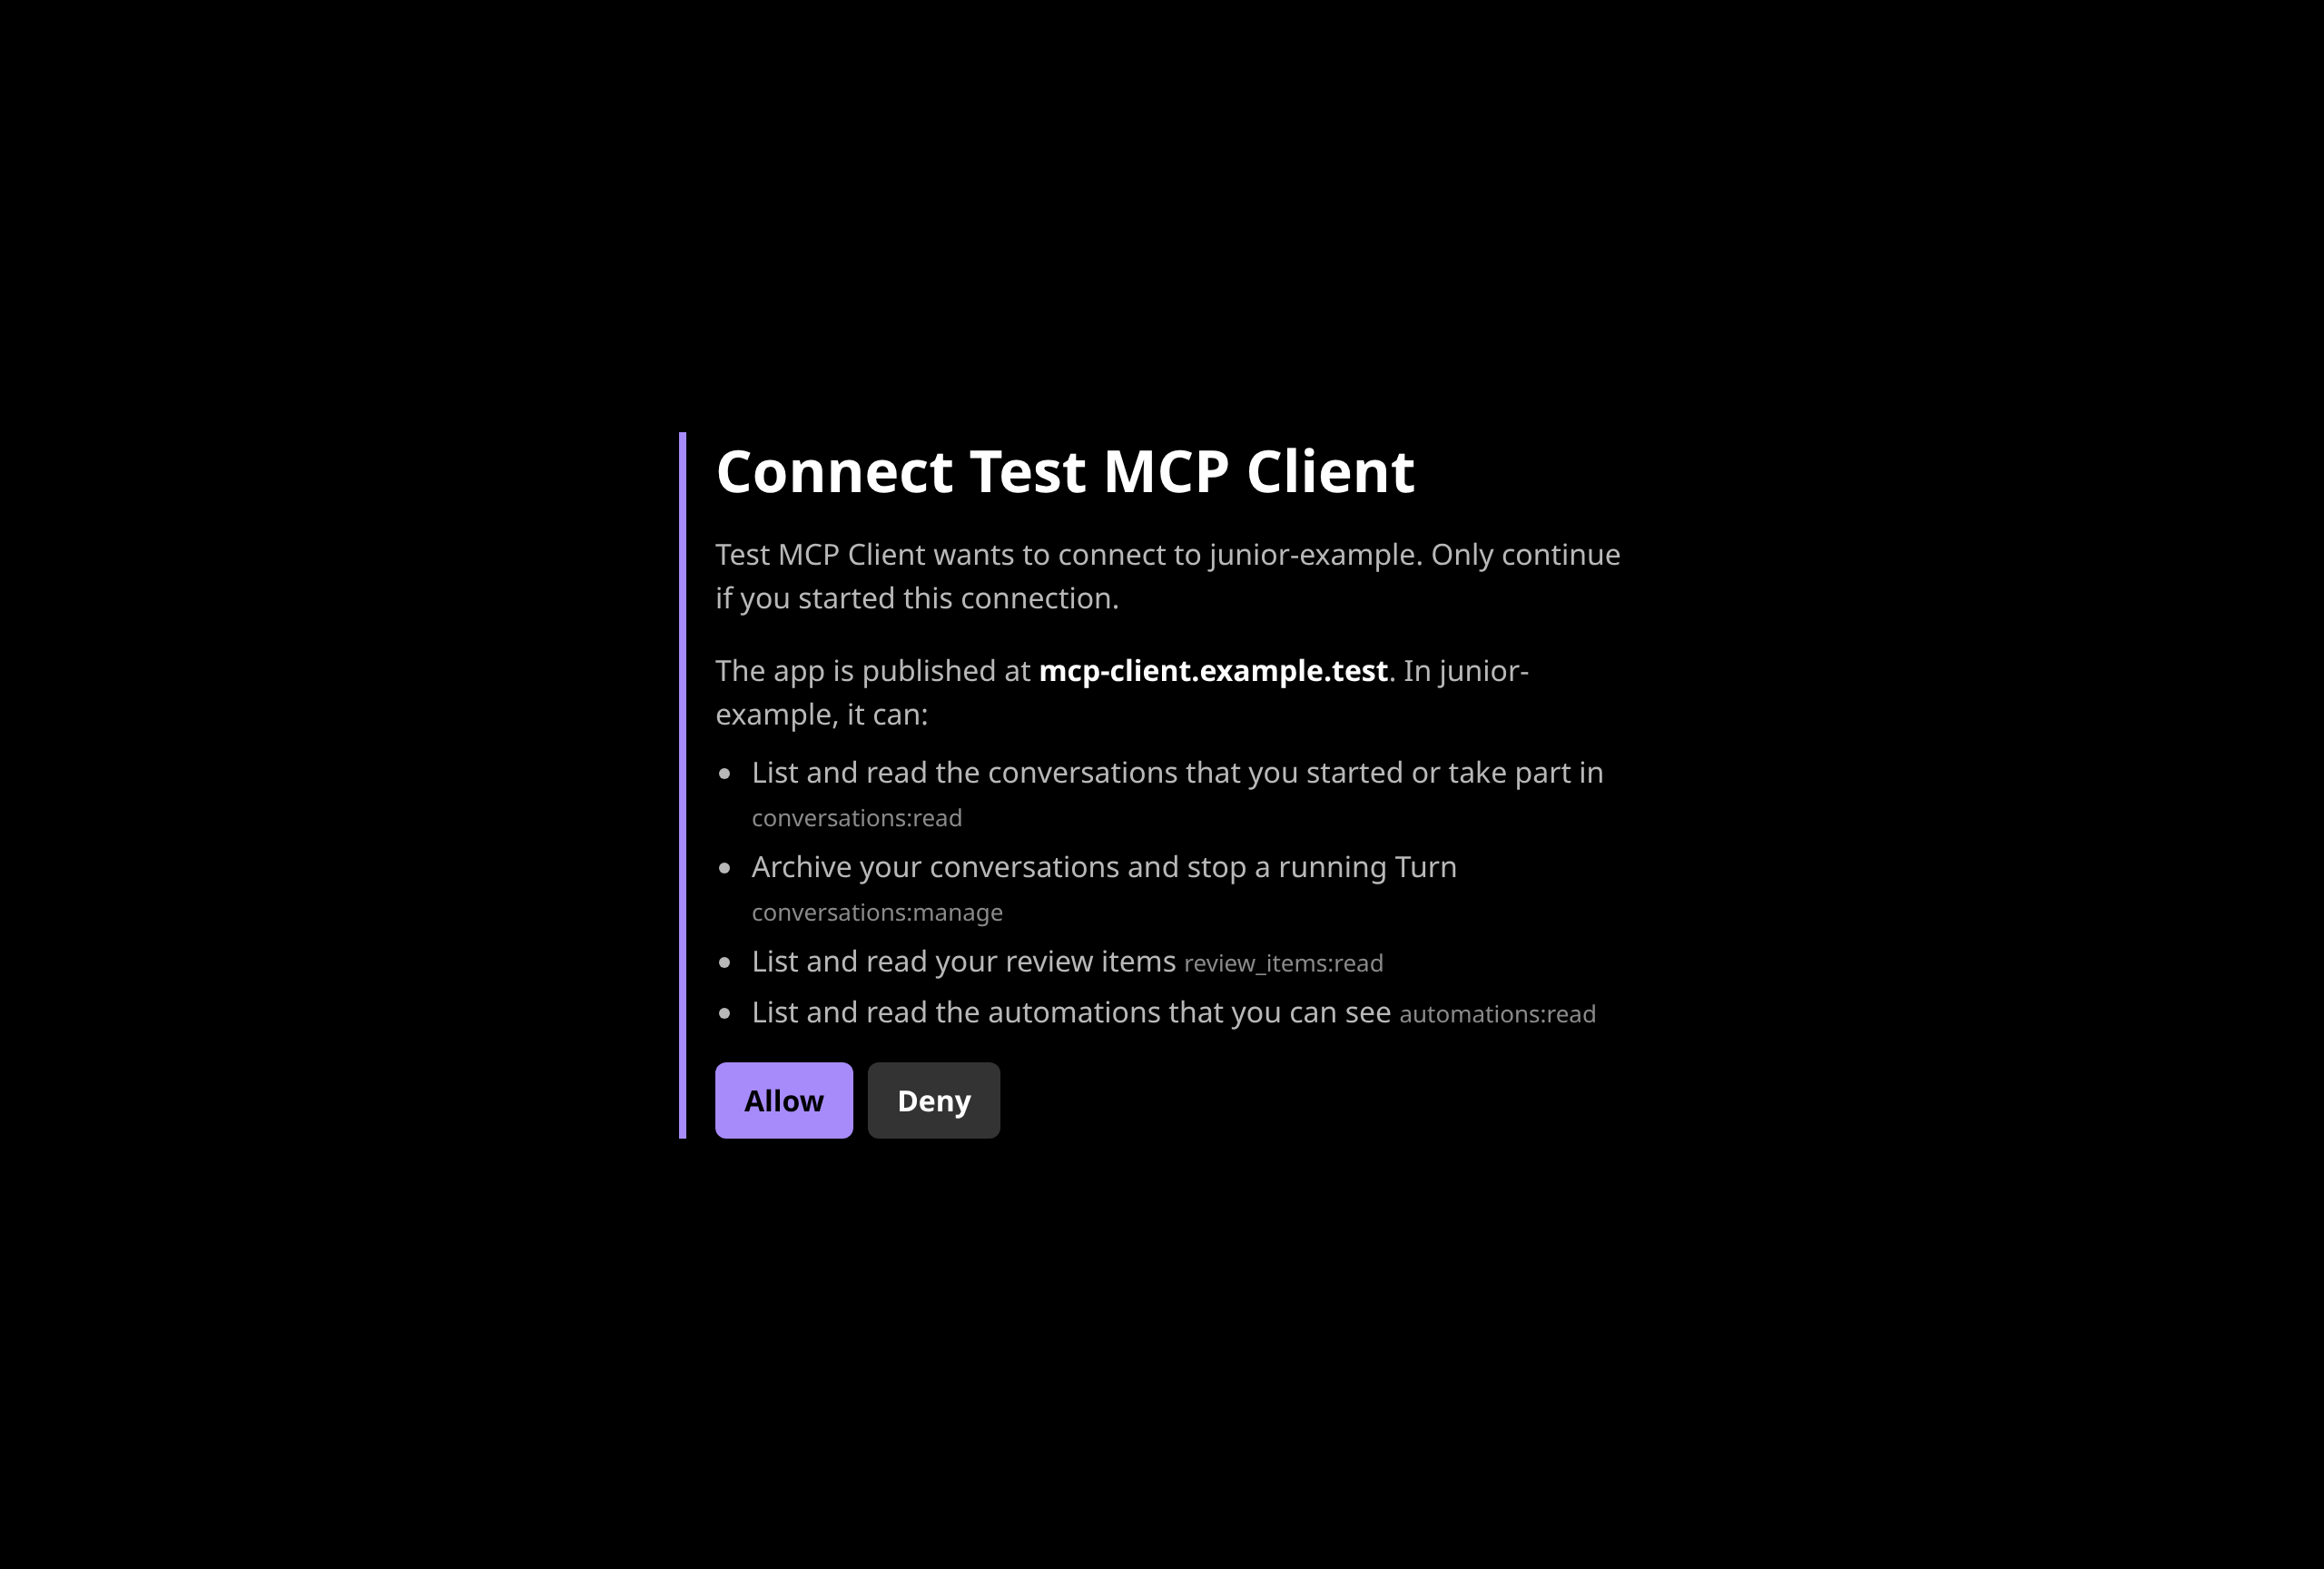
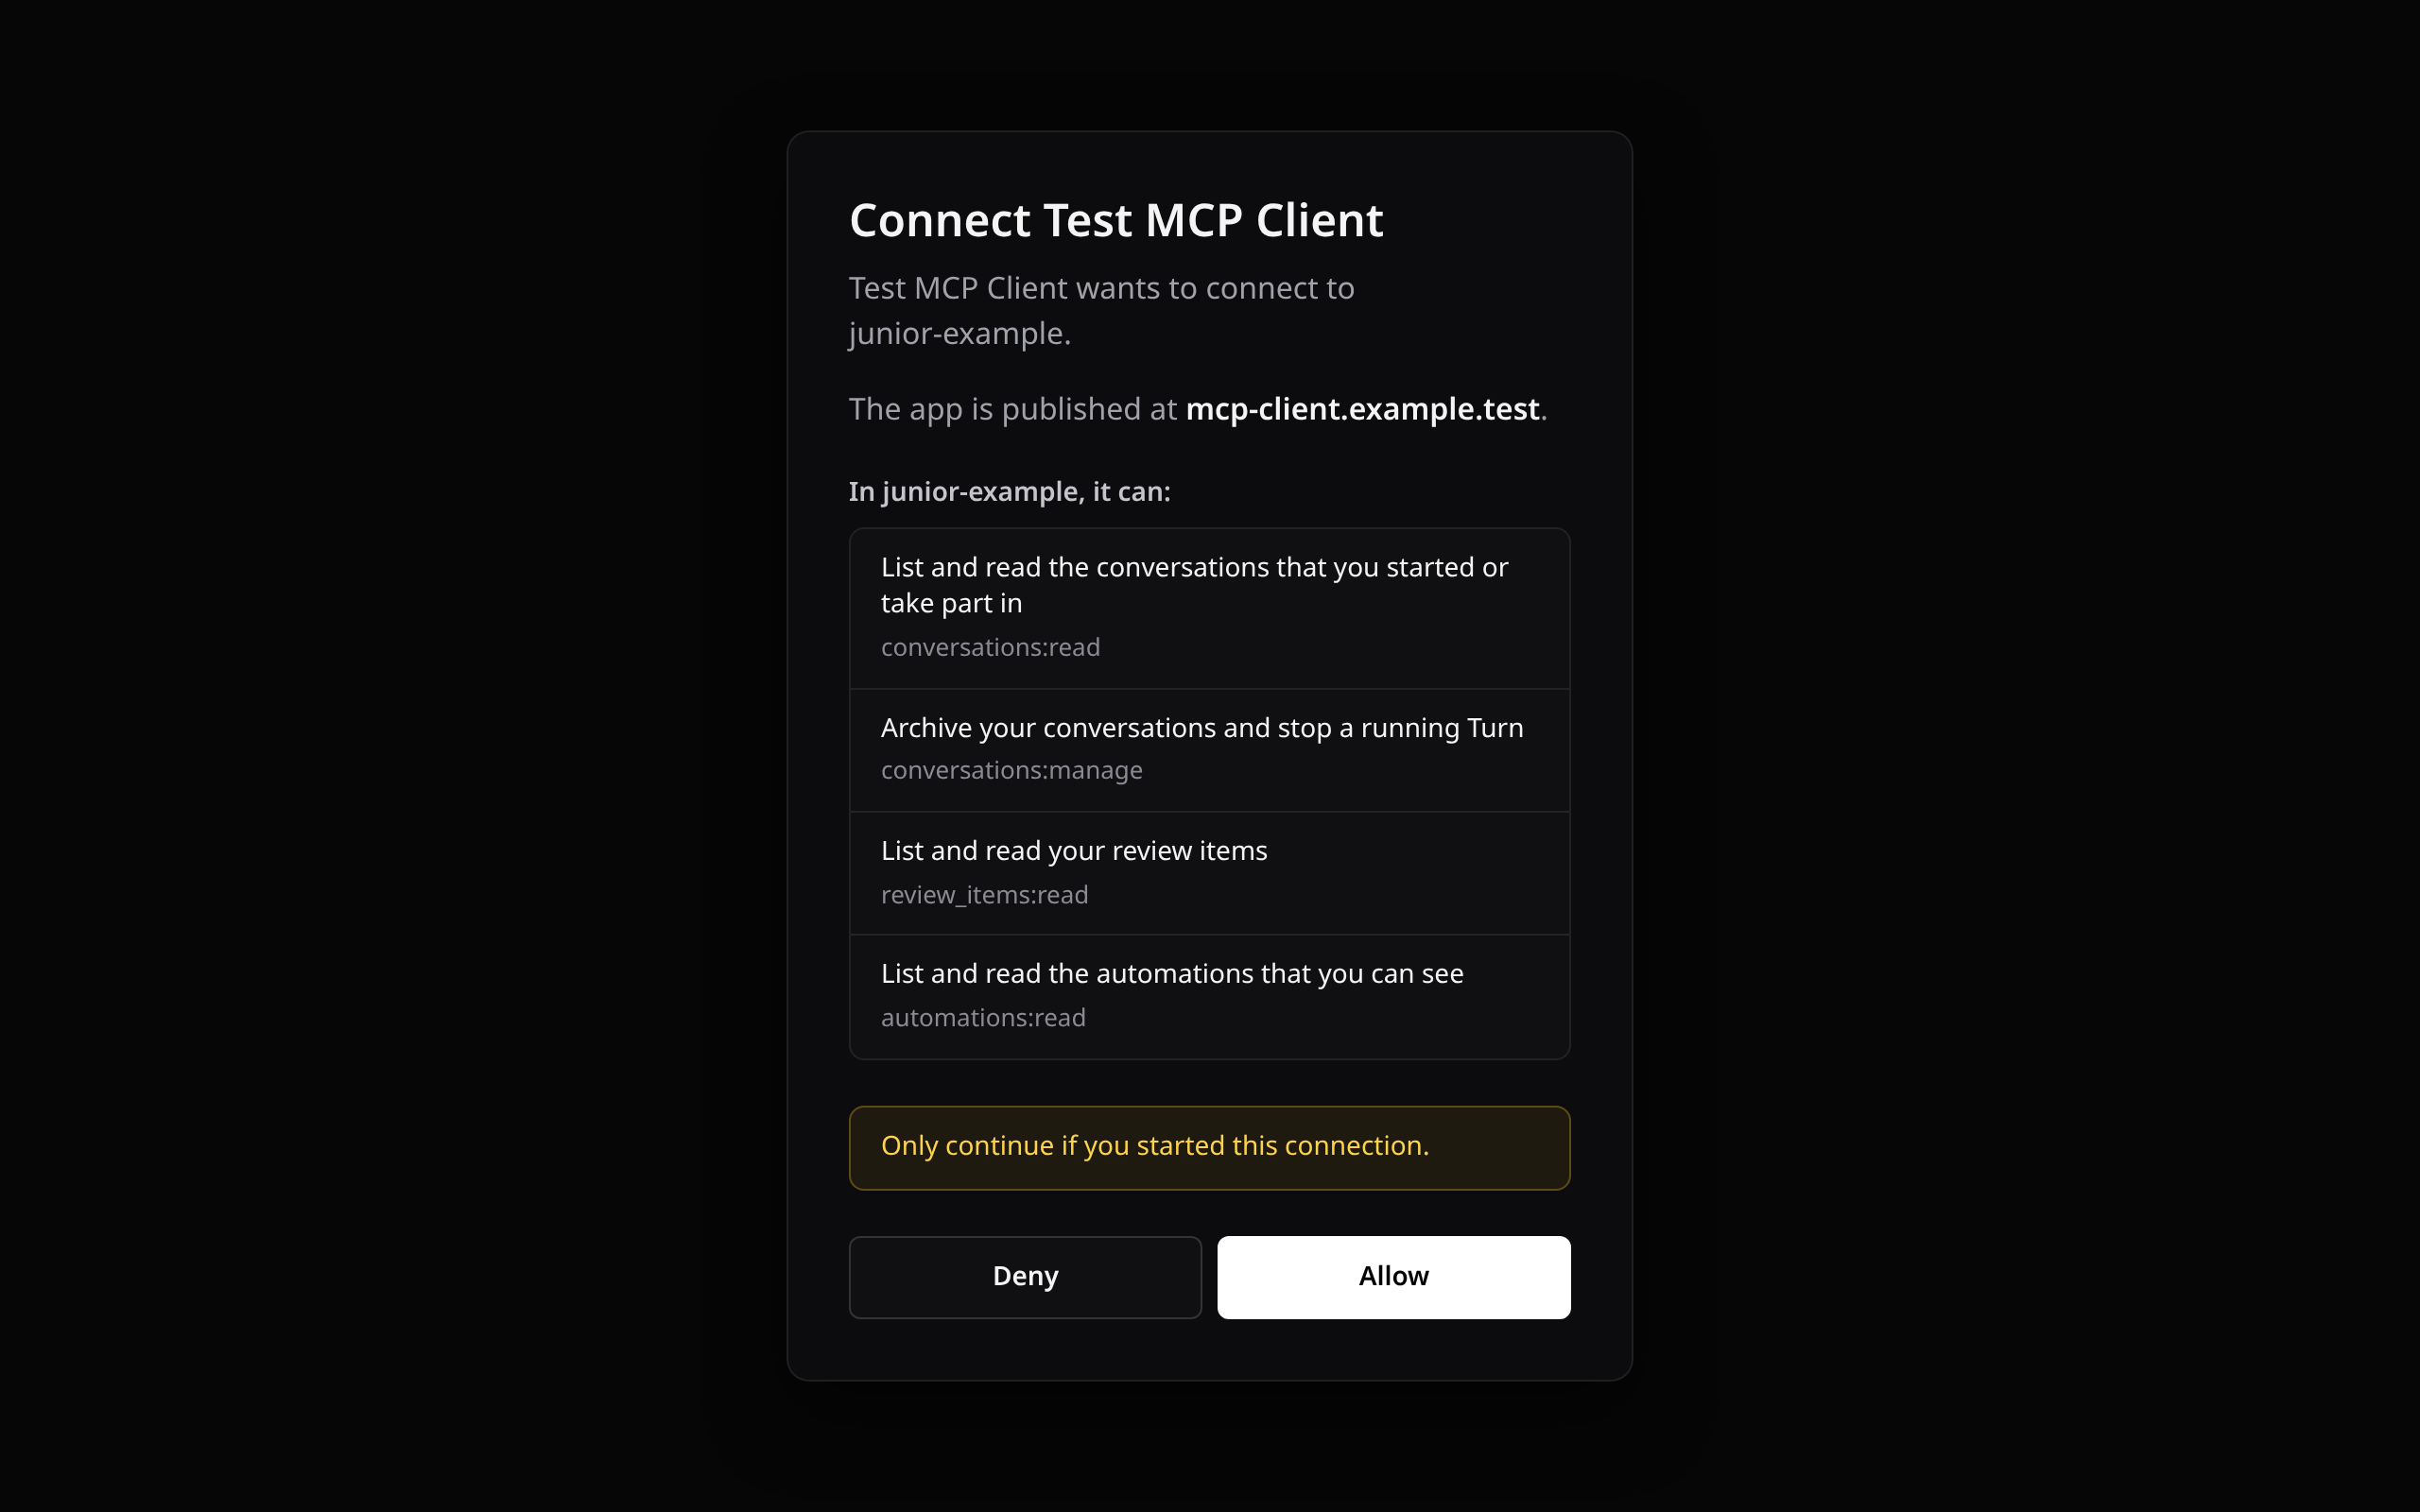
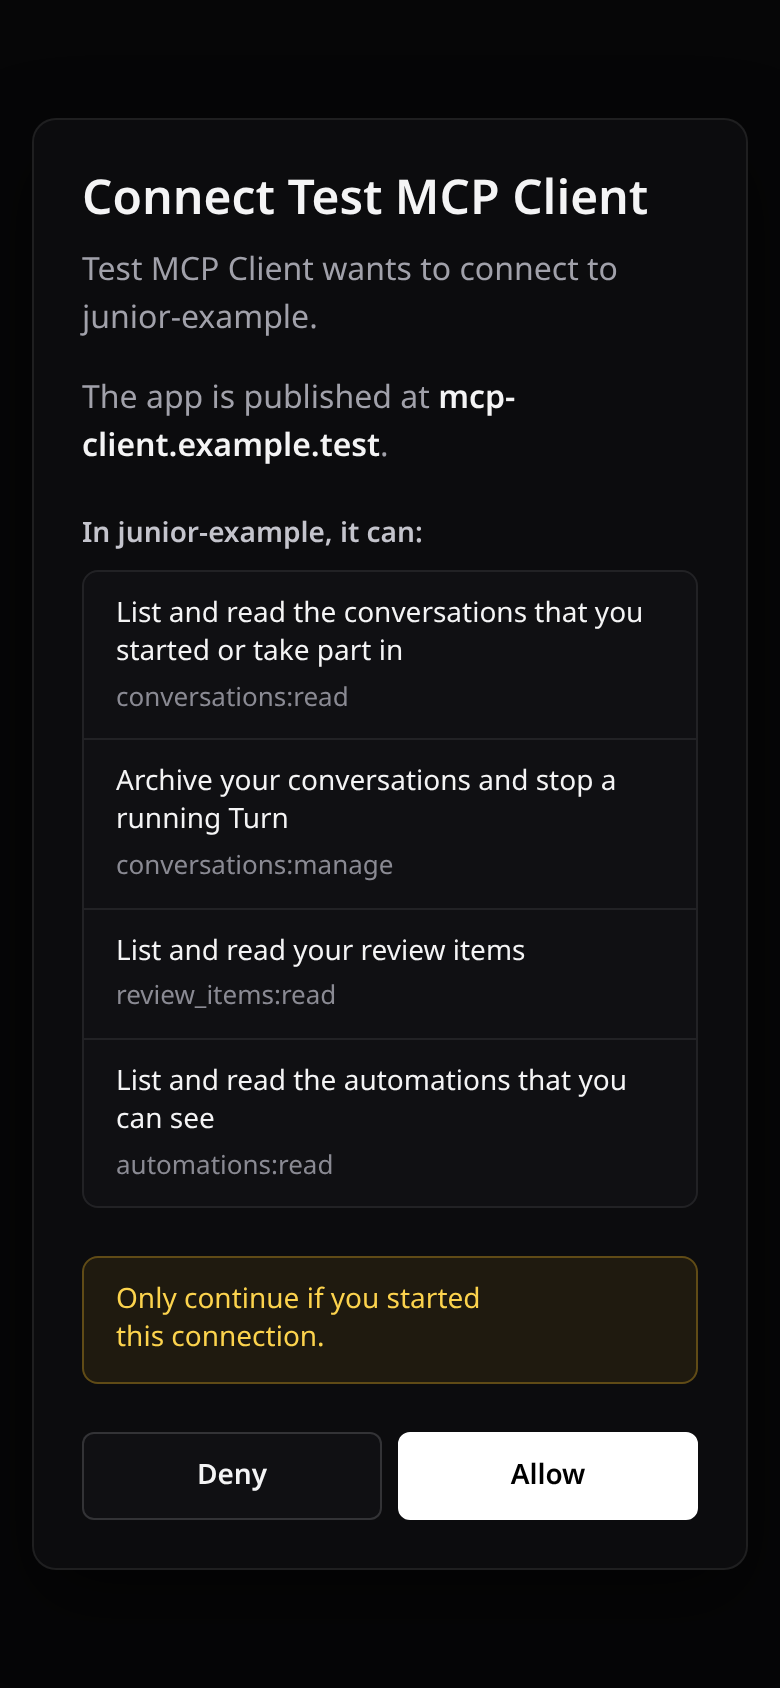
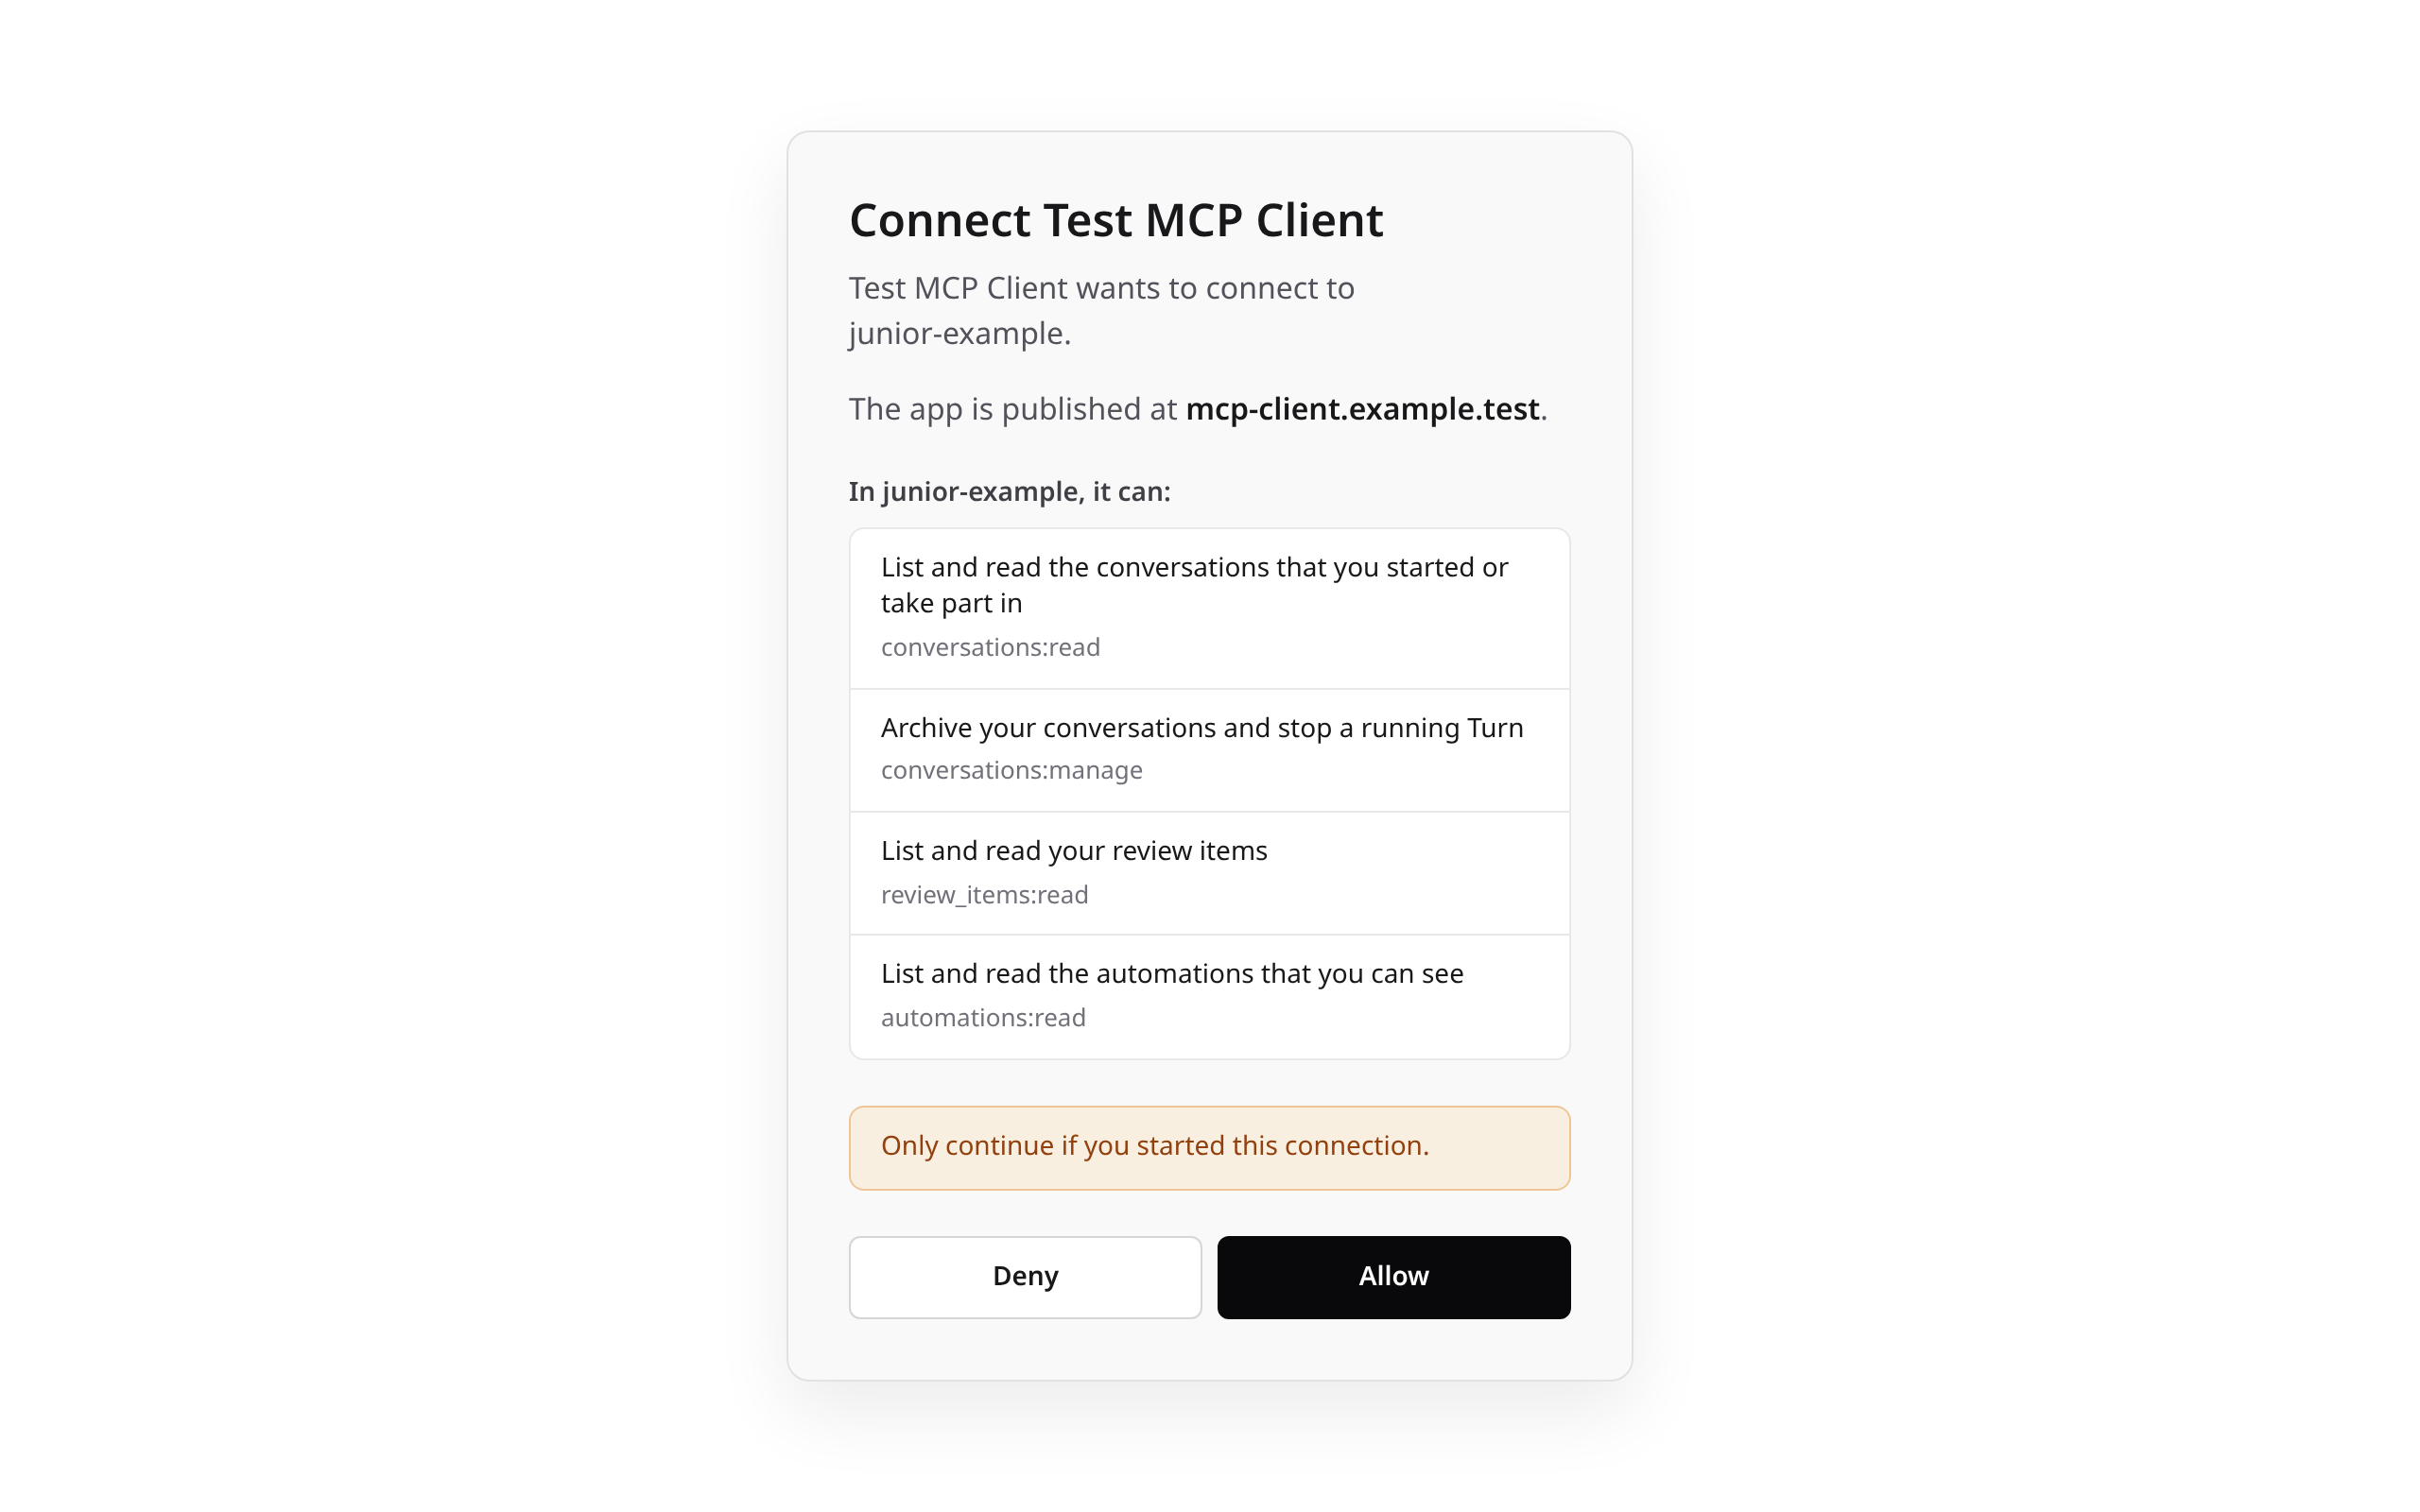
The MCP consent page was a bare text column. This PR gives it the
dashboard look. The ACP sign-in pages share the shell, so they change
too.

- `renderHtmlPage` now ships one inline `<style>` block with the
dashboard tokens (zinc canvas, panel card, white primary button,
lavender focus ring). It also has a `prefers-color-scheme: light`
variant. The page still loads no resources, so CSP is unchanged.
- Consent: the requested scopes show as a bordered list, each with its
scope id. "Only continue if you started this connection" moved into its
own amber callout. Deny and Allow are equal-width buttons, with Allow as
the primary one.
- Buttons and inputs are at least 44px tall and have visible focus
states. Inline `style=` attributes are gone from these pages.

Independent of the "Request blocked" fix in #2638, which only changes
the `referrer-policy` header.

| Before | After (dark) |
| --- | --- |
| <img
src="https://junior-prod.sentry.dev/public/artifacts/5ca6765e-8a88-4121-b215-336f7f2ccd7d.png"
width="420"> | <img
src="https://junior-prod.sentry.dev/public/artifacts/de8ea389-2126-43b7-ae8d-a6fa0c1da745.png"
width="420"> |

| Mobile | Light |
| --- | --- |
| <img
src="https://junior-prod.sentry.dev/public/artifacts/5ba26595-5801-461a-bca5-6fd3c70ea083.png"
width="200"> | <img
src="https://junior-prod.sentry.dev/public/artifacts/766c223b-887f-4217-8f73-934fa3b950ba.png"
width="420"> |

<!-- junior-request-attribution:start -->
via @dcramer.
<!-- junior-request-attribution:end -->

<!-- junior-session-footer:start -->
<!-- junior-conversation-id:agent%3A8c5086518f88cae99ab6f32f0c7427f9 -->

--

[View
Session](https://junior-prod.sentry.dev/conversations/agent%3A8c5086518f88cae99ab6f32f0c7427f9)
[[Sentry]](https://sentry.sentry.io/explore/conversations/agent%3A8c5086518f88cae99ab6f32f0c7427f9/?project=4510944073809921)

<!-- junior-session-footer:end -->

Co-authored-by: sentry-junior[bot] <264270552+sentry-junior[bot]@users.noreply.github.com>
Co-authored-by: David Cramer <23610+dcramer@users.noreply.github.com>
This branch was successfully deployed
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Clicking Allow on the MCP consent page always returned "Request blocked".
The page sets
Referrer-Policy: no-referrer. Under that policy, the Fetch spec has browsers sendOrigin: nullon a non-CORS POST. That includes a same-origin form submit.requestHasSameOriginthen fails, so every approve or deny got the 403 page. The ACP page uses the same check and works, because it doesn't setno-referrer.The fix switches to
Referrer-Policy: same-origin. The consent POST keeps its realOrigin. The redirect to the MCP client is cross-origin, so the client still gets no referrer, and the consent URL doesn't leak.The integration test missed this because the fixture hardcoded
Origin. The fixture now buildsOriginfrom the page's referrer policy, the same way a browser does. With the old header, 5 MCP route tests fail. With the fix, they pass.Reported in Slack: https://sentry.slack.com/archives/C0B595QDZLL/p1793750566935369
via @dcramer.
--
View Session [Sentry]